Control agent access. Keep the evidence.
Review features for identity-to-action attribution, default-allow policy checks, optional approvals, connection governance, and audit evidence.
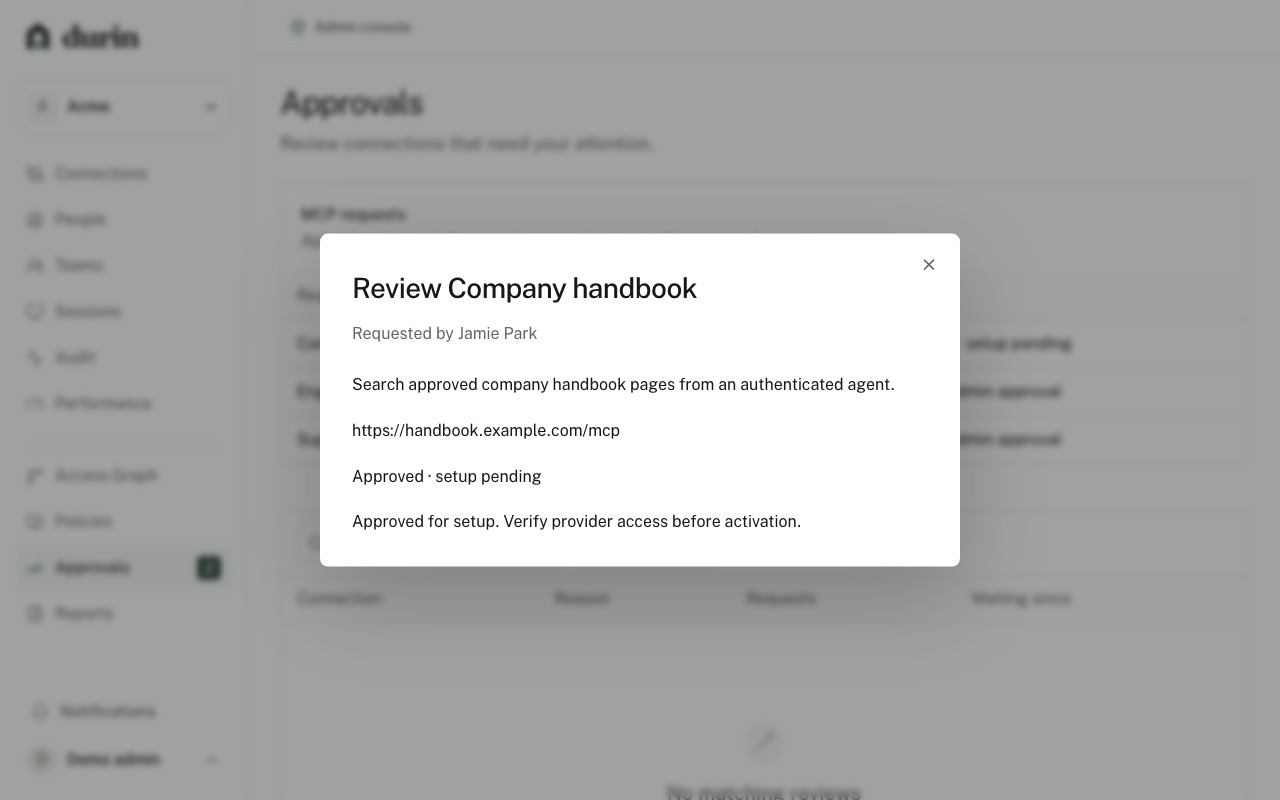
From a request to a reviewed connection.
Bring requests into view
Give your team a place to ask for a catalog MCP or a custom server. Administrators see what is being requested and why.
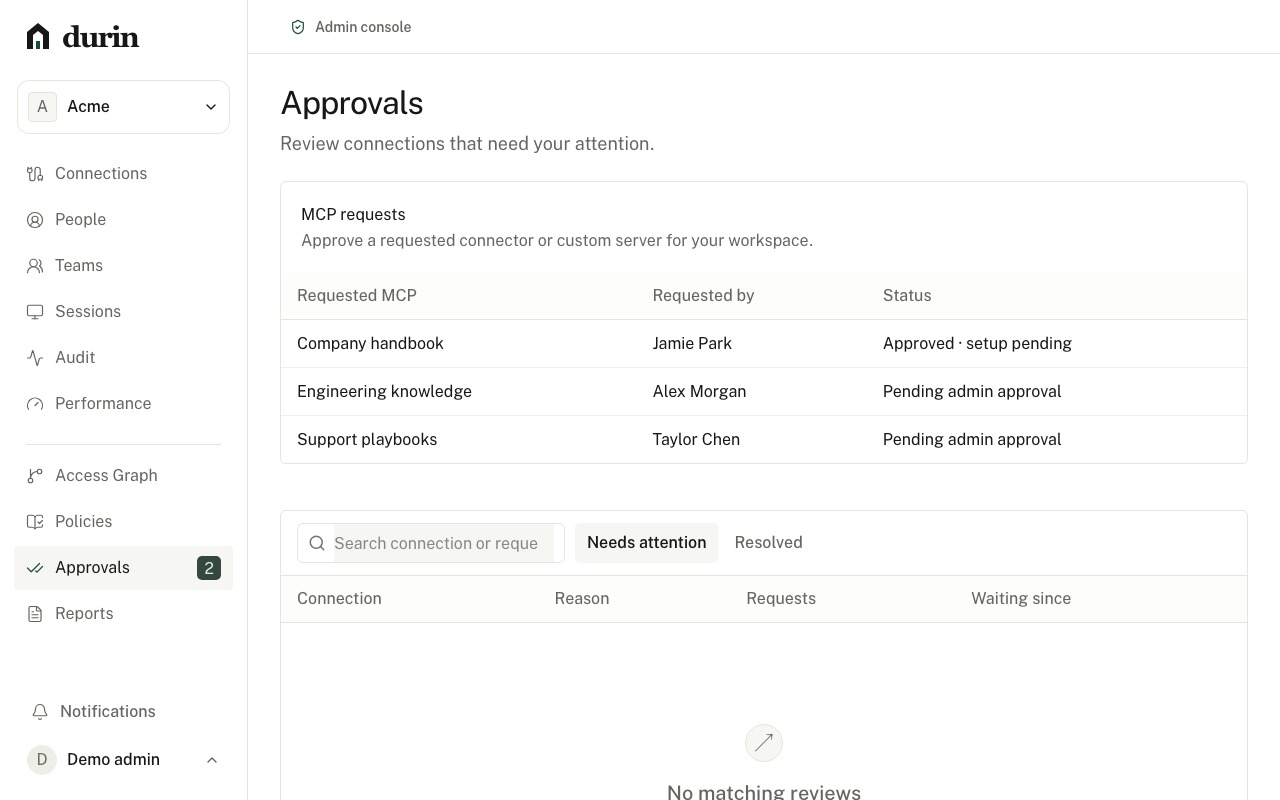
Make the next step explicit
Review the person, purpose, and server before approving setup. Keep approval separate from activation, then notify the requester when the connection is usable.
Make the boundary inspectable.
Durin combines gateway enforcement with identity, policy, approval, and evidence primitives so teams can inspect why an agent request was allowed and what happened next.
Identity to action
Attribute a request to the organization, environment, requesting person or service, client, connection, tool, resource, policy version, and execution result. Revocation is checked during the final authorization check.
Default allow with stricter controls
Use reviewed capability mappings and resource-aware policy. Sensitive actions can require independent approval or be disallowed while reads remain available.
Reviewed tools and evidence
Enforce the reviewed tool and resource set, record audit intent before dispatch, export authorized metadata, and preserve uncertain outcomes for follow-up. Live discovery, change diff, review, and activation remain deployment gates.
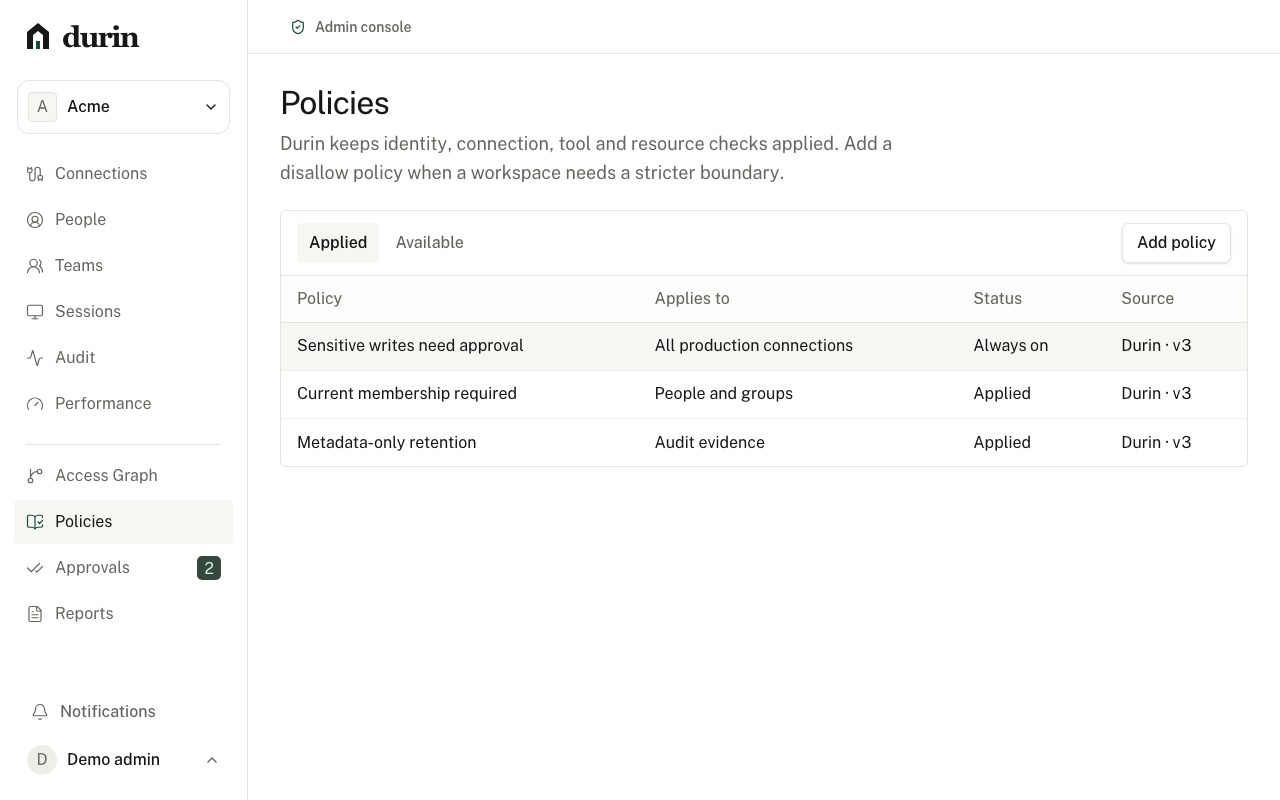
An allowed action still needs an outcome.
Allowed
The request passed policy. Dispatch can proceed.
Succeeded, failed, or uncertain
The execution result describes what happened upstream.
Attributable
Keep the initiating identity and decision context attached.
Put explainable controls to work.
Create an account to evaluate default-allow policy checks, optional review controls, scoped connections, and audit evidence.
Create an accountProduction connections use provider setup and trust review.