Every action has a boundary.
Follow a governed agent request from identity and policy through approval, execution, and attributable evidence.
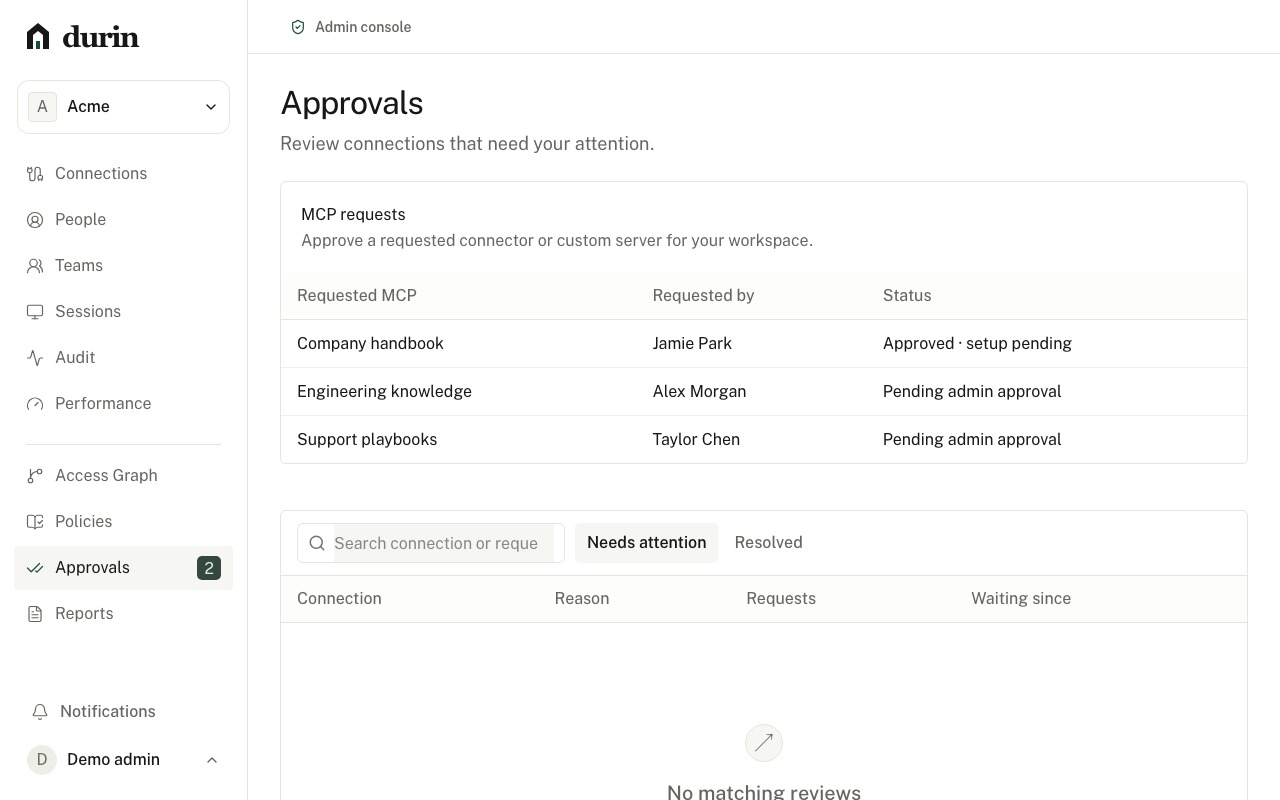
See what happens before and after the call.
Durin evaluates a request at the point where an approved agent asks to use a connected system. Policy can allow, deny, or require approval; a dispatched call can then succeed, fail, or remain uncertain.
Identify the request
Carry organization, environment, requesting person or service, authenticated client, connection, tool, and resource context into the decision. A self-reported client name is metadata, not permission.
Evaluate the policy
Default allow follows membership, client restrictions, connection and resource policy, reviewed capability mappings, and the upstream credential boundary.
Execute and record
Record intent before dispatch and store the outcome. Exact approvals bind arguments, schema and policy version, requesting identity, resource set, expiry, and execution count.
Explore platform.
Understand the governed request path and its controls.
How it works
See how identity, policy, approval, and execution fit together.
Features
Review controls for policy, approvals, connections, and evidence.
MCP gateway
Route supported MCP requests through Durin's governance boundary.
Integrations
Review client and upstream connection paths and production trust controls.
Trace an action from request to evidence.
Create an account to control access, review approvals, and follow each action through to its recorded outcome.
Create an accountProduction connections use provider setup and trust review.